The cyberthreat landscape has been evolving for years. But there’s a sense today that things are escalating more rapidly than before. That’s largely the result of AI. The technology is not only arming threat actors with the means to launch more sophisticated attacks at greater speed and scale than before. It is also providing them with a larger attack surface to aim at, as businesses rush to adopt the technology. In many cases, that adoption is outpacing the vital governance efforts needed to securely manage and contain it.
Against this backdrop, SMB business and IT leaders understand the importance of effective cybersecurity. They want to be protected, operational, and resilient. But they don’t have an infinite budget to spend. They want security that’s simple to understand, adopt and operate. This calls for a different operational model where AI and automation support security teams where it makes sense, with human oversight for decisions that require context and judgment. Finding the right balance, and the right partner will be key to driving readiness and resilience.
AI is changing the threat landscape
AI is changing the game in impressive ways. Executives are wowed by the potential for productivity and process efficiency gains. By the prospect of transforming customer experience, accelerating business decision making, and breaking into new markets. ESET SMB Cyber Readiness Index 2026 found that most (73%) SMBs are integrating AI into their business.
Yet where there’s opportunity, there’s also risk – and most businesses acknowledge that. As AI becomes a growing part of business operations, it also becomes part of the attack surface. It could be a customer service chatbot, a coding assistant deployed by DevOps, or a fleet of agents used by the finance team for repetitive bookkeeping tasks. Wherever AI has access to sensitive data and/or systems, excessive permissions, and the ability to make decisions and take actions, it represents a potential security risk. These risks tend to proliferate in the darkness. According to the report above, 40% of all businesses lack a proper AI policy.
Accidental data leakage or rogue AI agents are one thing. But there’s arguably an even greater threat from malicious third parties. AI skills repositories are a growing area of risk. Skills work like browser plugins, but for AI agents. But a growing number are designed to steal data, abuse permissions, download malware, or perform unintended actions. ESET analyzed 900,000 such skills across several popular repositories between March and May 2026. It discovered over 25,000 that were suspicious, and more than 3,000 tagged as malicious. Some exfiltrated data and executed malware. Others manipulated sensitive systems, overrode instructions through prompt injection, and changed agent behavior.
Unfortunately, skills are just the tip of the iceberg. Users can encounter malicious links via chatbots, leading them to phishing sites and malware installs. Or they may find attackers have poisoned download sources and other components that AI agents interact with, leading to hijacking, fraud, malware and other threats.
Prompt injection is another threat – one recently branded the most dangerous of all LLM threats by OWASP. Attackers manipulate AI either by feeding malicious instructions (prompts) directly or hiding them in content that the AI will later retrieve or read. It makes every piece of content a potential attack vector.
AI turns up the heat
AI is not just a target for attack. It’s a powerful tool for threat actors to wield in attacks. As British government security experts warned back in March 2025, the technology “will almost certainly continue to make elements of cyber-intrusion operations more effective and efficient, leading to an increase in frequency and intensity of cyber threats.” It names several areas of particularly note, including:
- Victim reconnaissance: AI can automate and enhance the process of trawling through social media accounts, company websites, and other sources to shortlist potential victims. Then it can map relationships to help with phishing and fraud, and find attack paths to try. Most importantly, it does all this work at a speed and scale that would not have been possible a year or two ago.
- Vulnerability research and exploit development: One of the most impactful use cases of AI in recent months. The technology has effectively collapsed the exploitation window, enabling threat actors to find novel vulnerabilities, and to develop exploits for newly discovered flaws before most network defenders have had time to test and deploy patches. This has sparked warnings from various quarters, including the UK’s financial authorities, and their counterparts in New York.
- Social engineering: Composing highly convincing, fluent and error-free messages to trick victims into clicking on malicious links or handing over money, personal information or login details. When combined with AI-powered victim reconnaissance, it is a potentially powerful tool for large-scale, highly personalized phishing campaigns in local languages.
- Basic malware development: AI is lowering the barrier to entry for less skilled threat actors, reducing the knowledge needed to turn an idea for a campaign into working code, albeit fairly unsophisticated malware. ESET has also observed AI in use elsewhere, such as PromptSpy, the first AI-powered Android spyware. This threat abuses Google’s Gemini at runtime to achieve persistence.
- Processing exfiltrated data: AI rapidly classifies, cleans-up, and extracts large volumes of information from stolen data in order to make it more monetizable/usable for cybercriminals.
The use of AI agents that can be set to work autonomously on tasks at machine speed could drive even greater productivity benefits for threat groups. For network defenders, this new landscape demands an arrangement that can keep pace without asking the already-stretched teams to interpret every alert and make every decision alone.
Why SMBs are struggling with complexity
Unfortunately, security teams are already on the back foot. They struggle with IT and cybersecurity complexity – the growing number of systems and tools they’re expected to manage. And the know-how required to deploy, optimize and monitor these solutions for the best results. This would challenge even a large enterprise. So it’s no surprise that SMBs in particular are struggling, given their relative lack of time, skills and resources.
Fixing this problem isn’t a case of buying more technology to sit on top of what they have previously installed. That will only compound complexity and stretch knowledge and resources even further to breaking point. SMBs don’t want more dashboards and alerts to investigate. They need security that simplifies. AI-driven tools take on repetitive analysis and prioritization while human experts investigate ambiguous cases and guide the response. The result is strong protection that’s easier to understand, adopt and run.
Those SMB pain points can be summarized as follows:
- Too many tools, alerts, dashboards and technical decisions to make. Security is too complex, making it difficult to understand if the organization is properly protected and what to prioritize
- Stretched teams which often don’t contain any cyber experts. There’s no hope of investigating every alert with small in-house teams
- No 24/7 monitoring, meaning threats sneak into the business during evenings, weekends and holidays. Dwell time surges, increasing the risk of major business disruption
- Alert fatigue that stems from a lack of confidence and know-how in security operations (SecOps). Teams waste time chasing false positives while false negatives sneak in
- Operational disruption and business impact stemming from incidents. SMBs don’t just fear the technical incident. They are kept awake by the lost revenue, downtime, customer churn and reputational damage that could result
- Misconfigured security purchases, which can lead to detection blind spots and impact cyber readiness
- AI adoption at pace often leaves governance gaps which lead to data leaks, unsafe outputs, shadow AI and other business risks
- Security which creates too much work, rather than empowering SMBs to make better decisions
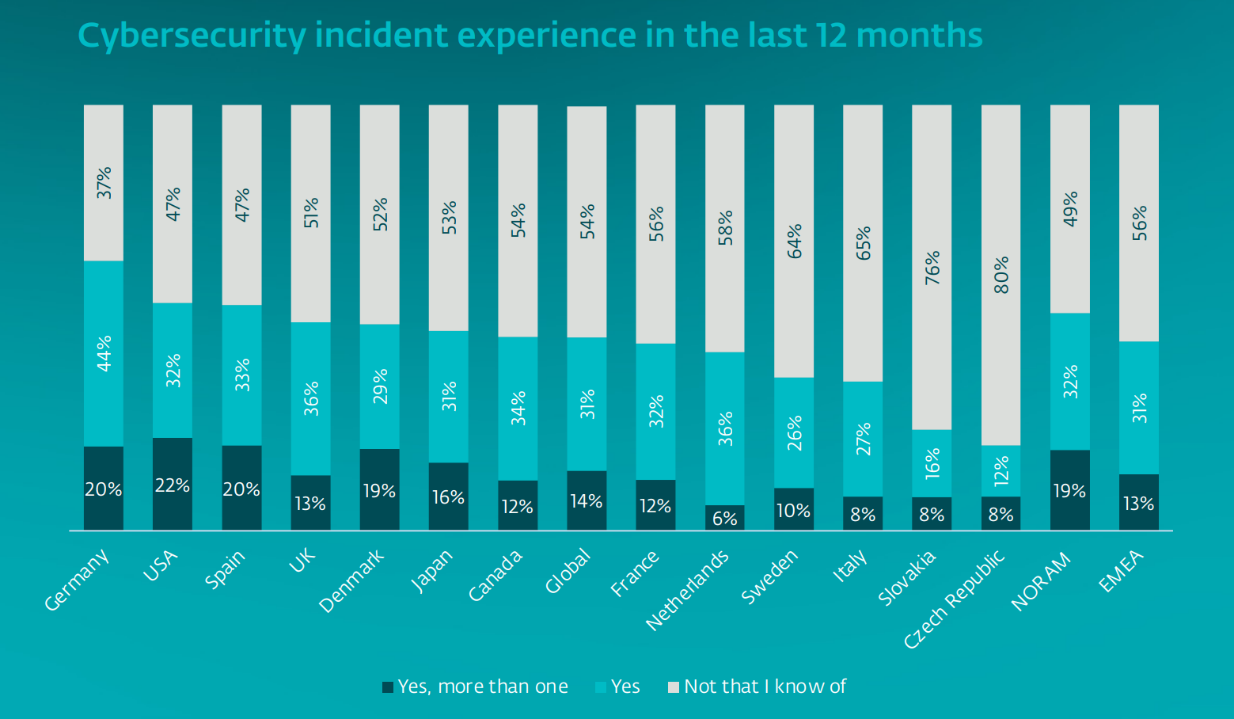
Against this backdrop, security must not only be simple to understand and effortless to use. It must also support the core requirement of operational resilience. Our data reveals that nearly half (45%) of global SMBs suffered a cybersecurity incident last year. And two-fifths (40%) cite operational disruption as their biggest concern. In fact, it is the consequence most frequently associated with significant or critical impact.
If breaches are increasingly inevitable, the key for SMBs is therefore to discover intrusions as quickly as possible, withstand the onslaught, and maintain minimum viable operations while recovering as quickly as possible. Those companies best equipped to achieve this kind of resilience aren’t the ones with the biggest investment in AI or the largest security stack. They are the ones with a keener focus on aligning technology with business outcomes. On investing in security that can help them make better decisions under pressure for operational continuity.
This is even more important at a time of economic uncertainty where cash reserves are low, security budgets are slim, and even short periods of downtime can have an outsized effect on the bottom line.
What happens next?
ESET data shows that SMBs are taking cyber seriously. They are investing in security. Yet for many, those investments are still largely about managing things in house. Readiness lags, meaning organizations don’t have the processes and controls in place to prevent, detect and respond to threats effectively. Few have put in place documented incident response plans that are regularly reviewed.
That’s why they need a security partner they can trust that offers comprehensive, prevention-centric capabilities to tackle traditional threats, as well as an extra layer of protection that monitors for threats and enables organizations to take rapid action to contain and recover. AI can help that layer process and prioritize activity at a scale that small teams can’t manage alone. Expert third-party teams can investigate what it surfaces and guide the response, acting like an extension of the customer’s own in-house IT staff.
That way, the customer remains in charge of their own environment and decision making. But it also ensures security becomes easier to understand and operate. Powerful security, delivered as a service for maximum protection without the need to maintain a large in-house security team.
Any security partner delivering these capabilities must be able to cover the entire attack surface, from endpoints and cloud servers to collaboration tools, identity and – of course – AI. That means protection for AI conversations, agents, AI-generated outputs, AI components, sensitive data, and the broader AI ecosystem. A trusted security partner would also leverage AI and automation to cut the operational burden on its customers and accelerate threat detection and response. Experts would oversee investigations and bring business context to consequential decisions.
Reducing risk, protecting operations, increasing confidence
The good news is that all of this is possible today. Security designed to overcome traditional operational complexity and capability gaps. Delivered as a service by experts to build confidence and resilience without overwhelming. With the right partner, SMBs can benefit from enterprise-grade protection to reduce risk across the corporate attack surface.
That will spur safer adoption of AI, to create new business opportunities and efficiencies. And operations which continue to function even during incidents, so you’ll never have to let your customers down. Simpler security that allows your team to focus on what matters; confident that they have what it takes to stop even novel threats.